TL;DR: AI agents are rapidly increasing the number of non-human identities with access to critical systems, data, and workflows, introducing new risks that organizations must address immediately. Instead of waiting for theoretical solutions such as an AI “kill switch,” security leaders need visibility, governance, and control over every identity within their environments. As the digital workforce continues to expand, organizations that can continuously identify, govern, contain, and recover compromised identities will be better equipped to adopt AI while maintaining security and resilience.
Recent developments have brought AI-related risks beyond security departments and into boardrooms, government discussions, and everyday conversations. Investigations involving OpenAI on platforms such as Hugging Face, as well as developments involving the Australian government, have raised concerns about how autonomous systems can access, share, and manipulate resources in ways their creators never intended. Meanwhile, lawmakers are discussing how organizations could stop a rogue AI agent if it poses a threat to critical operations or national security.
Much of this discussion revolves around the idea of an AI “kill switch.” Although the concept has attracted considerable attention, it remains largely theoretical. Organizations still lack clarity on what such a mechanism would involve, who would be responsible for controlling it, and how it would operate across different AI systems and environments.
At the same time, AI agents are already being deployed within organizations, accessing systems, data, applications, and workflows. Rather than waiting for future safeguards, security teams must focus on gaining visibility, implementing AI identity governance, and maintaining control over the identities these systems use today. Much of the immediate security risk lies within identity itself.
The 1996 film Multiplicity, starring Michael Keaton, offers an interesting comparison. In the movie, an overwhelmed employee creates clones of himself to increase productivity. Initially, the approach works well. However, managing the clones becomes increasingly complicated as each develops distinct behaviours, introducing new challenges involving visibility, accountability, and control.
Organizations are beginning to face a similar situation with AI agents. As businesses rapidly deploy these agents, they introduce a new category of non-human identities alongside the service accounts and APIs that organizations have been managing for years. These agentic identities offer significant opportunities for productivity and automation, but they also create the responsibility of managing an increasingly large workforce of trusted digital identities.
The AI Hiring Boom No One Is Tracking
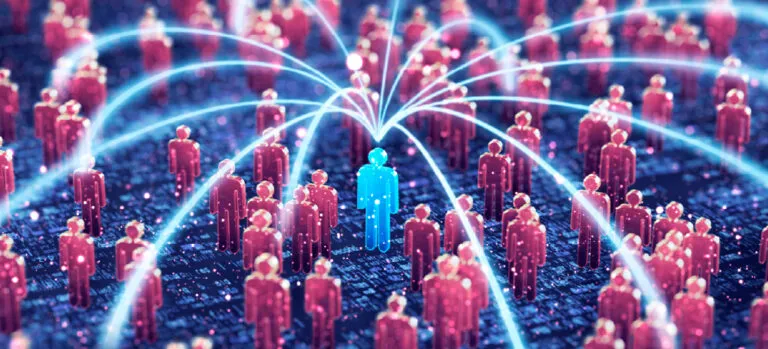
Imagine being able to instantly expand your organization's workforce by adding 100 employees for every existing employee. They operate around the clock, perform tasks at machine speed, and interact with dozens of systems simultaneously.
AI agents and automation are bringing a similar scenario into today's business environments. Every newly introduced agent requires some level of system access, yet AI identity governance is often unable to keep pace with this growth.
While businesses focus on the efficiency and productivity improvements, security teams must manage an increasingly complex trust environment.
This challenge is not limited to AI agents. Over the years, organizations have accumulated service accounts, automated workflows, machine identities, certificates, and APIs. AI is accelerating this existing development, causing non-human identities to grow at a much faster rate than the human workforce they support.
Attackers Have Noticed the Shift
Cyber attackers are increasingly targeting credentials, tokens, hashes, certificates, and machine accounts because trusted identities provide legitimate access pathways into critical systems.
When an identity is compromised, attackers may continue operating with its authorized permissions, making malicious activities significantly more difficult to identify.
The autonomous interactions between AI-powered systems introduce another layer of complexity. Security teams may find it challenging to distinguish legitimate machine-to-machine communications from malicious activities concealed within normal business operations.
You Cannot Govern What You Cannot See
Many security teams are finding it difficult to answer fundamental questions about their expanding population of non-human identities:
- Which identities currently exist?
- Who is responsible for each identity?
- What level of access and permissions do they have?
- How are they connected to critical systems and workflows?
- What would happen if one of these identities were compromised?
Finding answers becomes increasingly challenging as identity environments continue to evolve.
Most traditional AI identity governance approaches are built around periodic reviews and static inventories. However, non-human identities are constantly changing. They can be created, removed, inherit permissions, and interact with systems continuously.
By the time an organization conducts its next scheduled review, its identity environment may already have changed considerably.
From Visibility to Governance
Organizations need comprehensive visibility into every human and non-human identity across their environments. This includes establishing clear ownership and continuously monitoring for dormant accounts, unusual activities, privilege changes, and excessive access permissions.
However, visibility alone is not enough.
Security teams also require identity intelligence: the ability to understand relationships between identities, track how access permissions change over time, and identify where potential risks are emerging.
Applying least-privilege principles, lifecycle management, behavioural analytics, and continuous monitoring to AI agents and other non-human identities helps ensure that technological innovation does not move faster than an organization's ability to govern it.
Organizations must also recognize that not every attack can be prevented. Security leaders need the capabilities to contain compromised identities, restrict the spread of unauthorized access, and restore critical systems quickly when security incidents occur.
The Multiplicity Problem
In Multiplicity, creating the clones was only the first step. The real challenge emerged when it came to managing them.
Organizations are facing a comparable situation today. AI agents and other non-human identities can deliver substantial productivity improvements, but these benefits can only be sustained if organizations maintain proper control as their digital workforce continues to expand.
The increasing discussion surrounding rogue AI agents and AI kill switches highlights a broader reality: AI security is no longer just a technical concern. It has become a matter of business resilience, organizational governance, and board-level responsibility.
A practical AI kill switch may eventually become part of the solution. However, organizations cannot afford to wait for it while AI-driven identities continue multiplying across their environments.
AI identity governance is just as important as deploying AI identities in the first place. Organizations must understand what their digital workforce can access, determine who or what is accountable for its actions, and establish how quickly access can be restricted when something goes wrong.
About DT Asia
DT Asia began in 2007 with a clear mission to build the market entry for various pioneering IT security solutions from the US, Europe and Israel.
Today, DT Asia is a regional, value-added distributor of cybersecurity solutions providing cutting-edge technologies to key government organisations and top private sector clients including global banks and Fortune 500 companies. We have offices and partners around the Asia Pacific to better understand the markets and deliver localised solutions.
How we help
If you need to know more about The Multiplicity problem: Why AI identity governance is becoming a security imperative, you’re in the right place, we’re here to help! DTA is Quest Software’s distributor, especially in Singapore and Asia, our technicians have deep experience on the product and relevant technologies you can always trust, we provide this product’s turnkey solutions, including consultation, deployment, and maintenance service.
Click here and here and here to know more: https://dtasiagroup.com/quest/