Intercede MyID Authenticate provides enterprise-grade authentication designed to protect access to Windows, cloud and on-premise applications. Built around FIDO2 passkeys, MyID Authenticate enables phishing-resistant and passwordless authentication while supporting a range of additional authentication methods for different user and application requirements.
The solution integrates with existing enterprise environments through industry-standard protocols and can be deployed across on-premise, cloud and hybrid infrastructures.
Request for more information about the product/solution.
Our team will be happy to assist. Do allow us up to 3 business days to reply. Thank you for your patience.
Key capabilities include:

FIDO2 Passkeys – Passwordless and phishing-resistant authentication using device-bound or supported synced passkeys.

Secure Windows Logon- Extend strong authentication to Windows workstation and server logon, with support for online and offline authentication scenarios.

Enterprise Application Integration – Integrate with applications and infrastructure using SAML 2.0, OpenID Connect, RADIUS and other standard interfaces.

Identity & User Provisioning – Support integration with existing enterprise identity environments through standard identity-provider and SCIM-based user provisioning.
Flexible Authentication Methods – Support FIDO2, mobile push, OATH TOTP, hardware OTP and other authentication methods.
Centralised Policies Engine – Mandate passkeys for high-risk groups and applications & apply authentication requirements according to users, applications, devices and security policies.

Flexible Deployment – Support on-premise, cloud and hybrid deployment models, including environments requiring offline or air-gapped authentication.

Offline-Capable – Support offline authentication across supported authentication methods, making it ideal for air-gapped, classified, OT and field environments where cloud-based MFA may not be accessible. Provides offline MFA as a core capability, not a bolt-on.

PQC Ready – MyID Authenticate is designed with post-quantum readiness in mind, with its database able to be encrypted using the post-quantum algorithm ML-KEM. Further PQC capabilities are planned for future product releases.
Swissbit + Intercede PQC Authentication
Intercede and Swissbit are working together on an end-to-end FIDO2 passkey approach designed to incorporate Post-Quantum Cryptography (PQC) into the authentication chain.
As organisations prepare for the future impact of quantum computing, authentication credentials and the cryptographic technologies protecting them will become an increasingly important consideration.
The collaboration combines:
Swissbit Hardware
Secure hardware supporting FIDO2 passkeys and hardware-backed credentials.
Intercede MyID Authenticate
Credential issuance, management and authentication capabilities across the credential lifecycle.
Post-Quantum Cryptography
An approach designed to strengthen cryptographic protection against future quantum-computing threats.
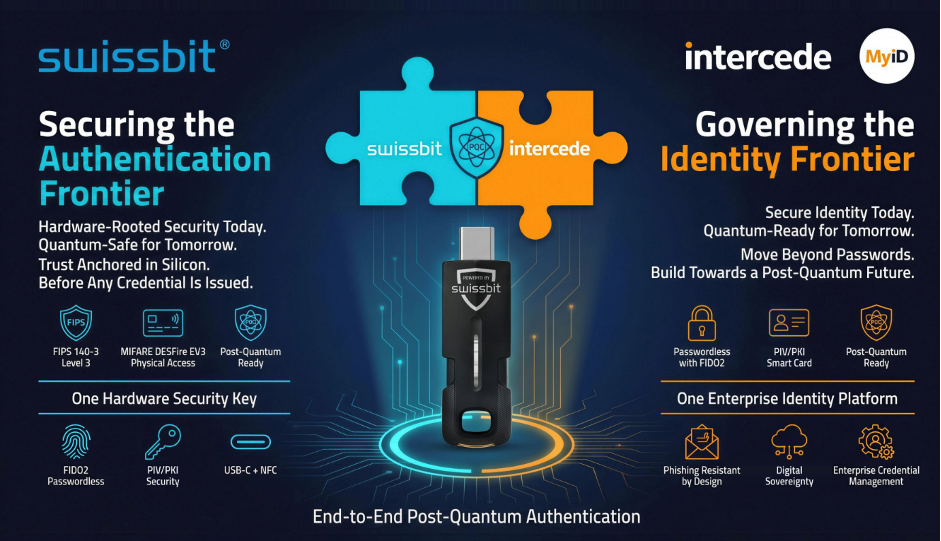
Towards Post-Quantum Authentication
Post-Quantum Cryptography
An approach designed to strengthen cryptographic protection against future quantum-computing threats.
Together, the technologies are intended to provide a path from secure hardware and credential management through to phishing-resistant authentication, while allowing organisations to build on existing FIDO2 and PKI investments as PQC standards and products and enterprise requirements mature.
From FIDO2 Today to Quantum-Ready Authentication
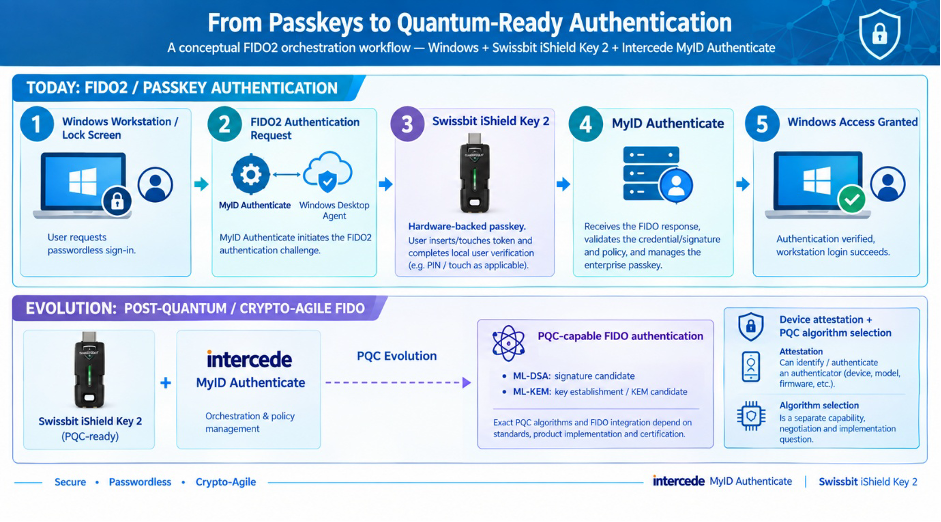
Organisations do not need to wait for the quantum era to begin strengthening authentication.
A practical approach is to establish a strong authentication foundation today using hardware-backed credentials, FIDO2 passkeys and centralised credential management, while preparing the environment for the adoption of post-quantum cryptography as standards, products and enterprise requirements mature.
With MyID Authenticate already PQC Ready, organisations can establish a modern authentication foundation today while preparing for further PQC capabilities as they become available.
DT Asia can help organisations evaluate their existing authentication environment and identify opportunities to strengthen authentication today while preparing for future PQC requirements.
About Us
From hardware appliances to software solutions and training, DT Asia understands cybersecurity challenges and can deliver solutions that help detect & identify, protect & secure, authenticate & authorise, and degauss & destroy.
Contact Us
Address
21 Bukit Batok Crescent,
#02-72 WCEGA Tower,
Singapore 658065
Phone
+65 6266 2877