Securing your sensitive data in one place should not be difficult. RC Devs enables you to have more flexibility by having highly configurable authentication schemes when implementing MFA (Multi Factor Authentication). RC Devs has been trusted by thousands of companies, including Fortune 100 companies, making it the preferred access security platform for many organizations.
Designed both for modern enterprises and SMEs, our Open OTP Suite helps you to secure all sensitive data from everywhere. Now working from anywhere is totally safe with RC Devs. Staying ahead at hyper competitive market is possible with us. DT Asia presents you with inventiveIdentity and Access Management technology while still offering a cost-effective option.The perfect solution for a smart organization like yours.
Tìm hiểu thêm về sản phẩm/giải pháp.
Rất vui được hỗ trợ Quý khách! Xin mời để lại thông tin và chờ phản hồi từ chúng tôi trong vòng 3 ngày làm việc. Trân trọng cám ơn Quý khách!

Multi Tenancy

Delegated Administration

Full Web & API Based

Modular Architecture

Hardware Security Module

Mobile Device Friendly
OpenOTP
OpenOTP is more than a Multi-Factor Server. It is a multi-factor middleware, a Swiss army knife of authentication, featuring an extensive array of 2FA methods like RADIUS, SAML, web-plugins and vast range of APIs, that integrates with any enterprise application or service whether in the cloud or on-premise. It supports both hardware and software token to suit in different environment according to organisation security policies. Other than the variety of integration tunnels and 2FA token support, RCDevs provides multiple authentication protocols that include OTP (SMS, email, software authenticator, hardware token) and U2F.
OpenOTP provides interfaces including SOAP, REST, JSON-RPC and RADIUS. The native SOAP API is extremely simple and is provided with a WSDL service description file. It is also very easy to implement OpenOTP One-Time Password and/or U2F functionalities into your existing web applications. Additional integration software from RCDevs provide support for Windows, ADFS, Linux and even Wifi access.

SpanKey
SpanKey is a centralised SSH key server for OpenSSH where the public keys are stored in your central LDAP directory (ex. Active Directory). With SpanKey there is no need to distribute, manually expire or maintain the public keys on the servers. Instead the SpanKey agent is deployed on the servers and is responsible for providing the users’ public keys on-demand.
The SpanKey server provides per-host access control with “server tagging”, LDAP access groups, centralised management from the RCDevs WebADM console, shared accounts, privileged users (master keys) and recovery keys. It supports public key expiration with automated workflows for SSH key renewal (via Self-Services).
TiQr Server
TiQr Server provides easy SOAP, REST and SON-RPC interfaces. The SOAP API is provided with WSDL service description file. It is also very simple to implement TiQR login into your existing web applications.
With RCDevs TiQR Login Server, you can authenticate users on:
- Web applications (Java, PHP, ASP, Python, .Net)
- OpenID-enabled websites (with RCDevs OpenID Provider)
- SAML and Google apps (With SimpleSAML Plugin)
- Cloud SSO applications (SalesForce, SugarCRM, GoToMeeting)
- OpenSSH (with TiQR PAM module)
- Web-based products (SugarCRM, Joomia, RoundCube)
- Any other systems (using our simple integration libraries)
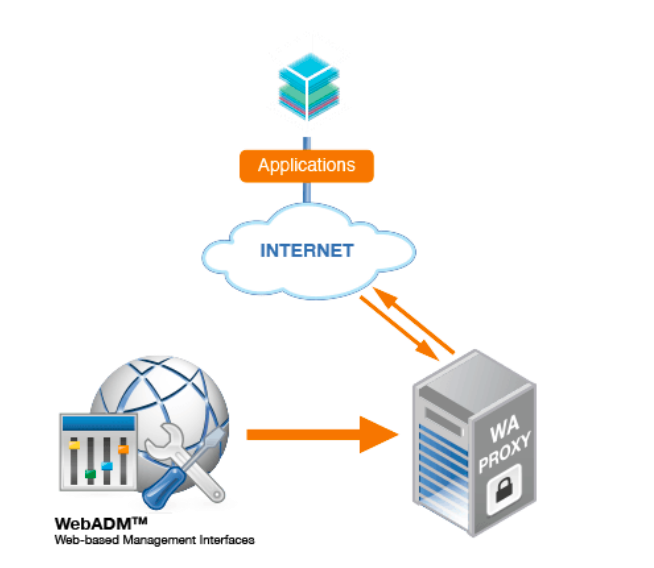
WAProxy
RCDevs provides a reverse-proxy server called WAProxy which takes care of publishing the selected end-user portals on the internet. WAProxy is provided as an RCDevs software package and is very easy to deploy and configure. With WAProxy you can choose which application portals should be available from your proxy server.
With RCDevs’ TiQR solution, the mobile devices must communicate with the TiQR server. WAProxy provides the required TiQR mobile communication endpoint. You also do not need to make your TiQR server’s API be accessible from public networks.
If you use OpenOTP with Universal Two-Factor (U2F), the FIDO-U2F design implies that an Application ID communication endpoint (called AppID) must be available under a public URL under your company’s DNS domain. WAProxy also provides the U2F AppID endpoint service.
Về Chúng tôi
Từ các thiết bị phần cứng đến các giải pháp phần mềm và đào tạo, DT Asia thấu hiểu các thách thức về an ninh mạng và có thể cung cấp các giải pháp giúp phát hiện & nhận diện, bảo vệ & bảo mật, xác thực & cấp phép, cùng với khử từ & hủy vật lý.
Liên hệ Chúng tôi
Địa chỉ
21 Bukit Batok Crescent,
Tòa nhà WCEGA #02-72,
Singapore 658065
Điện thoại
+65 6266 2877